5 October 2026
Shadow AI on Mobile Is a Governance Problem for Malaysian Organizations
Your Mobile Device Management (MDM) policy covers the device. It says nothing about what an app on that device is quietly sending to an AI model hosted somewhere else.
That gap has a name now, Shadow AI, and Zimperium’s 2026 Global Mobile Threat Report puts real numbers behind how large it already is. In this article, we break down what Shadow AI actually looks like on mobile, why it deserves a closer look against Malaysia’s Cyber Security Act 2024, and why closing this particular gap starts with visibility and governance.
Executive Summary
- 45% of employees are now regular users of AI on their corporate devices, authorised or not, up from 15% the year before.
- Of those users, 67% are doing it through non corporate accounts, meaning the organization has no visibility into the session, the account, or where the data goes.
- The most common data type submitted to unauthorised AI tools is source code, followed by images and other structured data. In 3.2% of violations, employees uploaded research and technical documentation, a direct intellectual property exposure.
- Mobile makes this worse than the laptop version of the problem, no browser extension or corporate login is needed to reach the same clipboard, storage and camera that an approved work app uses.
- Malaysia’s Cyber Security Act 2024 places new emphasis on risk visibility and reporting for organizations designated as operating National Critical Information Infrastructure (NCII), and the accountability principles it reflects are relevant well beyond that group.
- MDM and DLP controls don’t cover what an app on a device sends to an AI model, and there is less tooling built to catch it on mobile at all. Most enterprises also have no policy governing AI use on personal devices, which makes governance the place to start.
What Shadow AI Actually Is, in Plain Terms
Shadow AI is what happens when employees use AI tools on company devices without those tools being approved, reviewed, or even known to the security team. It’s rarely intentional harm. Someone wants to move faster, so they paste a chunk of code into a chatbot to debug it, or drop a document into an AI tool to summarise it. The productivity gain is real. So is the fact that nobody in the organization knows where that data went afterwards.
Zimperium’s data shows this is now mainstream behaviour, not an edge case. 45% of employees are regular AI users on corporate devices, and two thirds of that usage happens through personal, non corporate accounts. That means even organizations with an official, sanctioned AI tool still have a much larger amount of unsanctioned use happening in parallel, invisibly.
Why Mobile Makes This Harder to Catch
A GenAI app installed on a phone doesn’t need a browser extension or a corporate login to reach the same clipboard, storage and camera that a work app on the same device uses. The same behaviours that put data at risk on a laptop apply just as easily on mobile, with one difference. There is less tooling built to catch it on mobile at all.
The type of data at risk is exactly what you’d expect from a workplace: source code is the single most common thing submitted to unauthorised AI tools, followed by images and other structured data. Research and technical documentation showed up in 3.2% of violations Zimperium tracked, which is a direct intellectual property exposure, not just a policy breach.
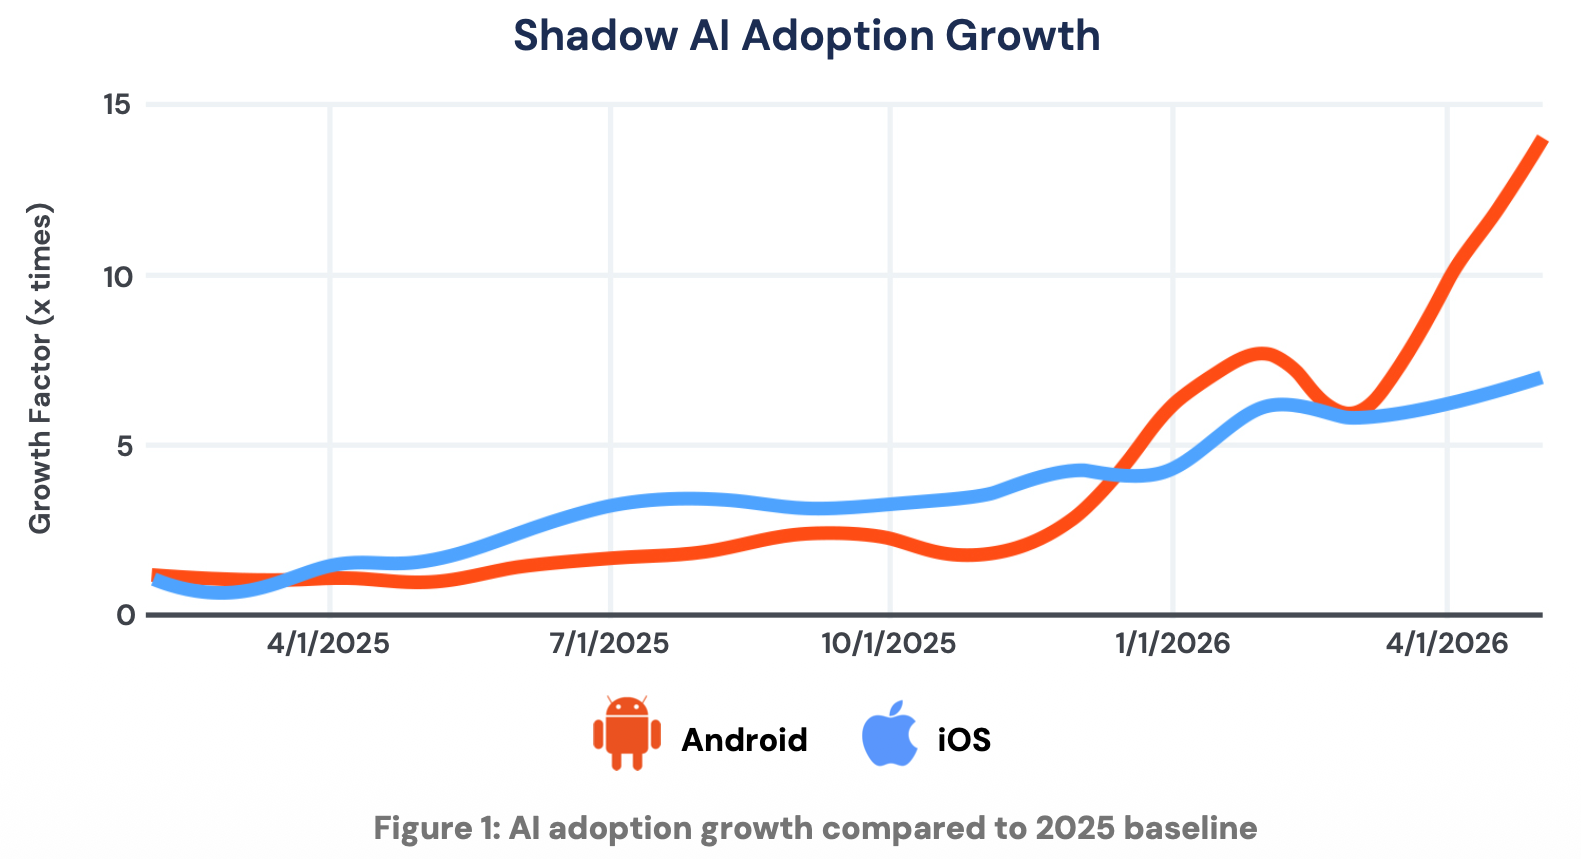
There’s a second version of this problem too. A growing share of the business apps employees rely on daily now ship with a GenAI feature built in. These apps were likely approved once, but never reviewed again when the AI capability was added. Zimperium’s zLabs data shows AI adoption in business apps growing 136%, and AI embedded apps overall up 14x on Android and 7x on iOS. An app your security team signed off on last year may not be the same app it is today.
Why Visibility and Governance Come First
Mobile Device Management covers the device, not what an app on it sends to a model hosted elsewhere. MAM and MDM policies with Data Loss Prevention controls do work within their scope, but they only cover the managed side. On unmanaged BYOD devices with no MAM enrollment, none of this applies at all. An employee can still photograph a screen, upload a research file from the device’s storage, or copy code into a GenAI app. As one line in the report puts it, “the data doesn’t need to be copied to leave. It just needs to be seen.”
Knowing which apps are on a device is not the same as knowing what they do. A Mobile Device Management platform can tell you which apps are installed and what version they run, but not what those apps access or what they leak. That is the visibility gap: most enterprises can’t see which apps have added an AI model, what data reaches it, or when a feature they already approved quietly started using one. It is not a tooling gap you patch with better DLP. Every app carrying an AI model, whether embedded, personal or unapproved, has to be vetted the same way.
Where the Cyber Security Act 2024 Comes In
The Cyber Security Act 2024, officially gazetted by the Attorney General’s Chambers and enforced by the National Cyber Security Agency (NACSA), was built around a fairly simple idea, organizations that hold or manage critical or sensitive systems need to actually know what their risk exposure looks like, and be able to demonstrate that to regulators when asked. Shadow AI sits directly against that principle.
For organizations designated as operating National Critical Information Infrastructure, the Act introduces obligations around risk assessment, audits, and incident reporting. Shadow AI complicates all three. You cannot meaningfully assess a risk you cannot see. You cannot audit a data flow that never touched an approved system. And if sensitive data left the organization through an unsanctioned AI tool, it may not even register as an “incident” under existing detection processes, because nothing was technically breached, the data simply walked out through a channel nobody was watching.
This isn’t legal advice, and every organization's specific obligations under the Act depend on its designation and sector. What we’d encourage is a conversation with your compliance function about whether your current risk assessment process accounts for AI usage on mobile devices at all. For many organizations, right now, the honest answer is no.
A Parallel Consideration Under PDPA
Separately from the Cyber Security Act, Malaysia’s Personal Data Protection Act remains relevant here too. If an employee pastes customer information, contact details, or other personal data into an AI tool the organization never approved, that data has left the organization’s control in a way the PDPA’s principles around data processing were never designed to accommodate. It’s a second reason this gap deserves board level attention, not just an IT policy update.
Four Questions for Your Next Security Review
- Does our AI usage policy extend to personal and BYOD devices, or only company issued ones?
- Do we have a process for re-reviewing approved apps when they add new AI capabilities?
- If asked to demonstrate our risk visibility into AI usage today, could we actually produce an answer?
- Who in our organization actually owns this policy, and does it reach past IT into compliance, legal and HR?
Closing the Gap Starts With Visibility and Policy
Given everything we’ve just mentioned, the starting point is visibility, plus a policy that reaches every device employees use for work, including personal ones, paired with a clear answer to who owns it. That’s a governance exercise. Defining what’s allowed, extending existing AI and data policies to mobile and BYOD, and building a process to vet apps, including when they change.
Vigilant Asia is a certified partner delivering Zimperium’s Mobile Threat Defense platform. The policy itself is a decision for your own compliance and legal teams, and our role is giving them the visibility to make it with.
What Shadow AI Means for Mobile Compliance in Malaysia
Shadow AI didn’t arrive with a warning. It arrived quietly, through ordinary employees trying to get their work done faster, on devices that were never built for this level of scrutiny.
Against a regulatory backdrop like the Cyber Security Act 2024, the question isn’t whether this gap exists, Zimperium’s 2026 report confirms it does, it’s whether your organization has a policy that actually covers it, because you can’t govern what you can’t see.
If you’d like to understand what visibility into AI usage on your organization’s mobile devices currently looks like, get in touch with us for a conversation.